Your organisation holds personal data. The law now says you must be licensed for it.
Staff records. Customer details. Member lists. Patient files. Under the Cyber and Data Protection Act [Chapter 12:07], organisations that process personal data must be licensed as data controllers and appoint a Data Protection Officer.
We handle the whole thing — assessment, policies, licence application, DPO appointment and staff training — on one guided system.
- Every claim cited — Act 5 of 2021 · S.I. 155 of 2024 · CDPG 1 of 2025
- We come to you — online or at your offices, Zimbabwe-wide
- Free self-check, free sector guides, and a done-for-you route if you need it.
- Gap assessment
- Policy pack drafted
- Licence forms filed
- Team training booked
The risk is not the same everywhere. Here is what yours looks like.
POTRAZ has said it will inspect on a risk-based approach, starting with named priority sectors. Find yours below — the first ten are named first.
Banks & financial institutions
Account records, KYC files and transaction histories.
Microfinance & SACCOs
Member savings records and guarantor details, often held on spreadsheets with no access controls.
Insurance & brokers
Claims files routinely contain health data, which is special personal information under the Act.
Local authorities & councils
Ratepayer databases, licensing records and residents’ contact details held indefinitely.
Healthcare providers
Patient records are special personal information; consent and retention rules are stricter.
Mining enterprises
Employee biometrics, medical surveillance data and contractor records across multiple sites.
Churches & ministries
Membership rolls, giving records and pastoral notes — personal data, whether or not you call it that.
Schools, colleges & universities
Learner records concern children, who receive heightened protection under the Act.
Government ministries & agencies
Citizen data at scale, with statutory duties that go beyond ordinary controllers.
NGOs & PVOs
Beneficiary data is often sensitive and shared with donors across borders.
Retail, supermarkets & wholesale
Loyalty programmes and CCTV footage are both regulated personal data.
Hospitality, hotels & tourism
Guest registers, passport scans and booking histories retained far longer than needed.
Telecoms & ISPs
Subscriber data and traffic records sit under both licensing regimes at once.
Technology, software & fintech
Processor for clients and controller for staff — both need addressing.
Transport, logistics & couriers
Delivery addresses, recipient names and vehicle tracking on drivers.
Agriculture & agribusiness
Outgrower schemes hold farmer identity and payment data at real scale.
Manufacturing & industrial
Shift records, biometric clocking and occupational health files.
Construction & real estate
Tenant applications, credit checks and site access registers.
Legal practices
Client files are confidential and personal data — privilege does not exempt you.
Accounting, audit & advisory
You process payroll and personal financial data for every client you serve.
Recruitment, HR & payroll
Your entire product is other people’s personal data. Expect scrutiny.
Media, publishing & advertising
Source data, subscriber lists and audience profiling all fall in scope.
Security services
Access logs, guard vetting files and surveillance footage.
Debt collection & credit bureaux
Financial history data with a direct effect on people’s lives — high sensitivity.
Sports clubs & gyms
Member health declarations and biometric entry systems.
Funeral services
Deceased and next-of-kin records, often held in unsecured paper files.
Motor dealerships
Finance applications, identity documents and service histories.
Utilities & energy
Household consumption data linked to named account holders.
Professional associations
Member registers, CPD records and disciplinary files.
Small & medium enterprises
Even a handful of staff records brings you inside the Act. Size is not an exemption.
My sector isn’t listed
If you hold personal data about any identifiable person, the Act almost certainly applies to you regardless of sector. Ask RegAi and it will tell you plainly.
Four stages. We do the work, you approve it.
Discovery
A structured session to understand what data you hold, how it moves and where you stand. You receive a written summary and a prioritised action list.
Assessment
A full gap analysis against the Act and S.I. 155 of 2024, plus a data inventory and processing register. You receive a gap report, risk rating and register.
Preparation
Policies drafted for your organisation, DPO appointment documentation, and your licence application completed and submitted. You receive the policy pack, signed forms and filed application.
Readiness
Staff awareness training and a walk-through of what an inspection involves. You receive a training session and an inspection-readiness checklist.
What we do
- Assess your position against the Act and S.I. 155 of 2024
- Draft your policies, notices and internal procedures
- Complete and submit your licence application on your behalf
- Prepare DPO appointment documentation
- Train your team and prepare you for inspection
What we don’t do
- Take over as your data controller — that responsibility stays with you in law
- Guarantee a licensing outcome — that rests with POTRAZ
- Replace independent legal advice where you are in dispute or under investigation
- Sell you software you don’t need, or bill by the hour with no ceiling
Five questions. A plain-language read on where you stand.
Five short questions give an honest picture of whether the Act applies to you, whether you need a DPO, your realistic exposure, and the first three things to do.
This is general guidance, not legal advice. Your licence category is determined by POTRAZ on assessment of your application.
Ask anything about the Act. Get an answer with the source attached.
RegAi answers questions about who the Act applies to, what licensing involves, what a DPO does, what happens in an inspection, and what each sector should do first — with the source cited. It hands over to a human when a question needs one.
RegAi provides information about the law. It does not provide legal advice.
Most people would rather ask on WhatsApp. So ask on WhatsApp.
Ask your questions in the app you already have open — the self-check, your sector guide, straight answers with the section of the Act cited, and a hand-off to a human when needed.
Start on WhatsAppRead before you act. Plain-language guides on the Act and the inspections.
DP1 application form — fillable, printable and downloadable
The data controller licence application form, with guidance on how to complete it.
A single page for your sector — exposure, and the first three things to do.
Built sector by sector. Find yours and download the brief written for it.
What Zimbabwean organisations ask us
Plain answers to the questions businesses type into Google about the Cyber and Data Protection Act.

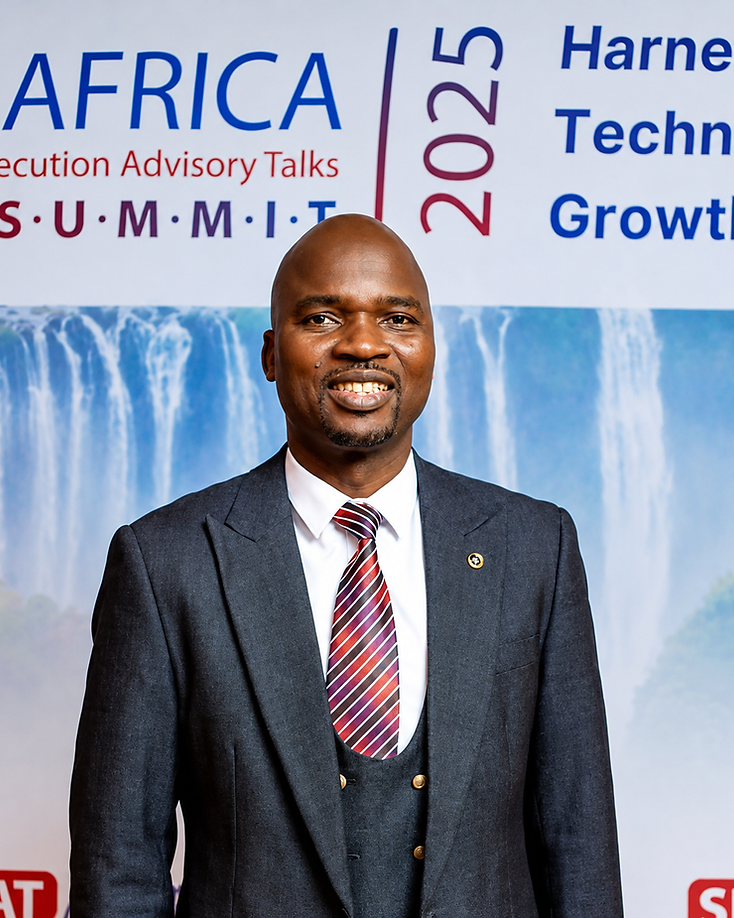
Legal credibility, paired with practical systems delivery.
Mr Moses Nkomo is our Data Protection Officer. With over 20 years in commercial legal practice and 19+ years lecturing Intellectual Property Law at the University of Zimbabwe, he brings the legal weight boards ask for when signing off on compliance.
As Acting Director of the University of Zimbabwe Intellectual Property Legal Support Centre, and in a leadership role at Donsa-Nkomo & Mutangi Legal Practice, his work spans IP generation, protection, commercialisation and enforcement — for corporates, institutions and organisations across Zimbabwe and beyond.
That mix is why this is not a generic tech tool. Legal credibility and practical systems delivery sit together: policies drafted, the officer appointed on paper, the register built and the application filed — overseen by someone who has done this work for two decades.
Forty-five minutes. You leave knowing exactly where you stand.
Held online or at your own offices — anywhere in Zimbabwe. You receive a written summary and a prioritised action list, whether or not you engage us.
- A clear read on your obligations in plain language.
- A written summary and a prioritised action list.
- An indicative timeline and scope for getting compliant.
- The full fee for our compliance bundle confirmed in the session.